

 Irenes (many)
all our love to the workers trying hard to restore Microsoft's services. that stuff is hard, and there must be an impossible stress level at this point
our feelings about the company itself are a different matter, but never let that make you forget class solidarity
 senanthic
Join #EFF to Celebrate the Life of Aaron Swartz
https://www.eff.org/deeplinks/2026/11/join-eff-celebrate-life-aaron-swartz
#aaronswartz #aaronswartzday
Serbia just elected the world’s brainiest parliament. Dozens of academics become politicians after the student group’s stunning victory.
https://www.science.org/content/article/serbia-just-elected-world-s-brainiest-parliament
Hey, that's cool. Canada seeking to become the EU's 1st associate member. Good for us.
https://www.cbc.ca/news/politics/european-union-canada-associate-member-von-der-leyen-9.7401989
 Sheril Kirshenbaum
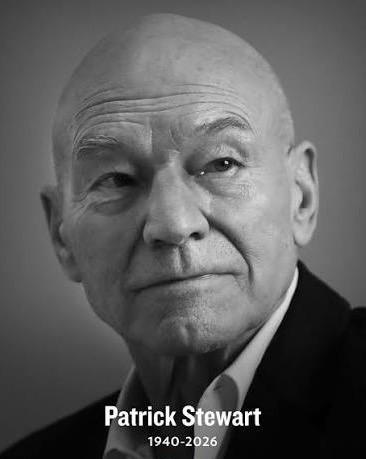
“I always have been optimistic about humanity's future. Always. Even at the most dismaying of times.”
- Patrick Stewart
Canadians Are Running Out Of Time To Oppose The Dangerous C-22 Surveillance Bill
@MozillaAI Love the direction you're going! What do you think about building an open cli + agentic coding harness that, by default, uses preferred/optimized local models or could optionally connect to Otari? I know we've got OpenCode, it's fine, but I see space for a Mozilla answer to this. #AI #Coding
 Ricky Mondello
If you actually read the “Passkeys are a trap. Do not use them.” post going around, you’ll find a transparent attempt to clumsily string together a conspiracy.
The post is predicated on the idea that a feature of WebAuthn called “attestation”, which is only used in high-assurance and usually corporate scenarios, and usually with physical hardware security keys, will be leveraged to hurt people, somehow.
The post posits that a website like X will bait and switch users: first, you get a passkey. Then, later, scary “attested” passkeys! This simply isn’t possible to do because attestation isn’t supported on the web for mass market, consumer authentication.
Attestation for passkeys (software-based, syncable credentials) is antithetical to their mass market goals, and would freeze out independent, non-corporate-backed credential managers. It’s an explicit non-goal of the designers of passkeys, who work together in a forum anyone can join.
And trust me, websites and apps like banks repeatedly asked for attestation at the beginning of the industry’s passkey journey. The platforms, browsers, and credential management apps have held firm that the goal of passkeys is reducing phishing and **not** some kind of trusted computing scheme. (And I will note: over my dead body!)
Besides the theory of the case being fundamentally wrong, there are several things that make the post disqualifying in terms of arguing something useful or important in the realm of security, privacy, and user authentication:
1. Intentionally presenting things that are complicated as inherently suspicious. (Delivering security by design can be complicated, yes!)
2. Describing TOTP as a “great solution” for adding security to a password-based account. When the most common threat model on the web is phishing (a word the post never mentions!), TOTP hardly buys you _anything_. TOTP is phishable.
3. Seeming to be unbothered by how many logical leaps are being taken without actually understanding the topic being discussed.
There are bad things happening in tech and untrustworthy people and companies do exist, but they’re largely in the AI space, not the “let’s stop people we love from getting compromised through phishing” space.
 Innocuous In Innisfil 🇨🇦
Good Morning #Canada
Depending on your latitude the #FallColours are on full display or getting ready to put on a show. If you're looking for the ideal #RoadTrip to experience this annual show then put the Agawa Canyon train tour on your list for next year (I think it may be too late for 2026). My wife and I took this train ride in the 80s and it was worth the day long investment.
#CanadaIsAwesome #TravelCanada #VintageTrains
Agawa Canyon
https://www.nationalgeographic.com/travel/article/agawa-canyon-ontario